Explore / 01
Fortinet FortiGate
Combine network connectivity and security policy in a FortiGate deployment. The appropriate model and security subscriptions are selected against your agreed design.
Firewall selection, configuration and lifecycle support for branch, office and remote-access environments.
Businesses replacing a firewall, opening branches or standardizing network protection.
Combine network connectivity and security policy in a FortiGate deployment. The appropriate model and security subscriptions are selected against your agreed design.
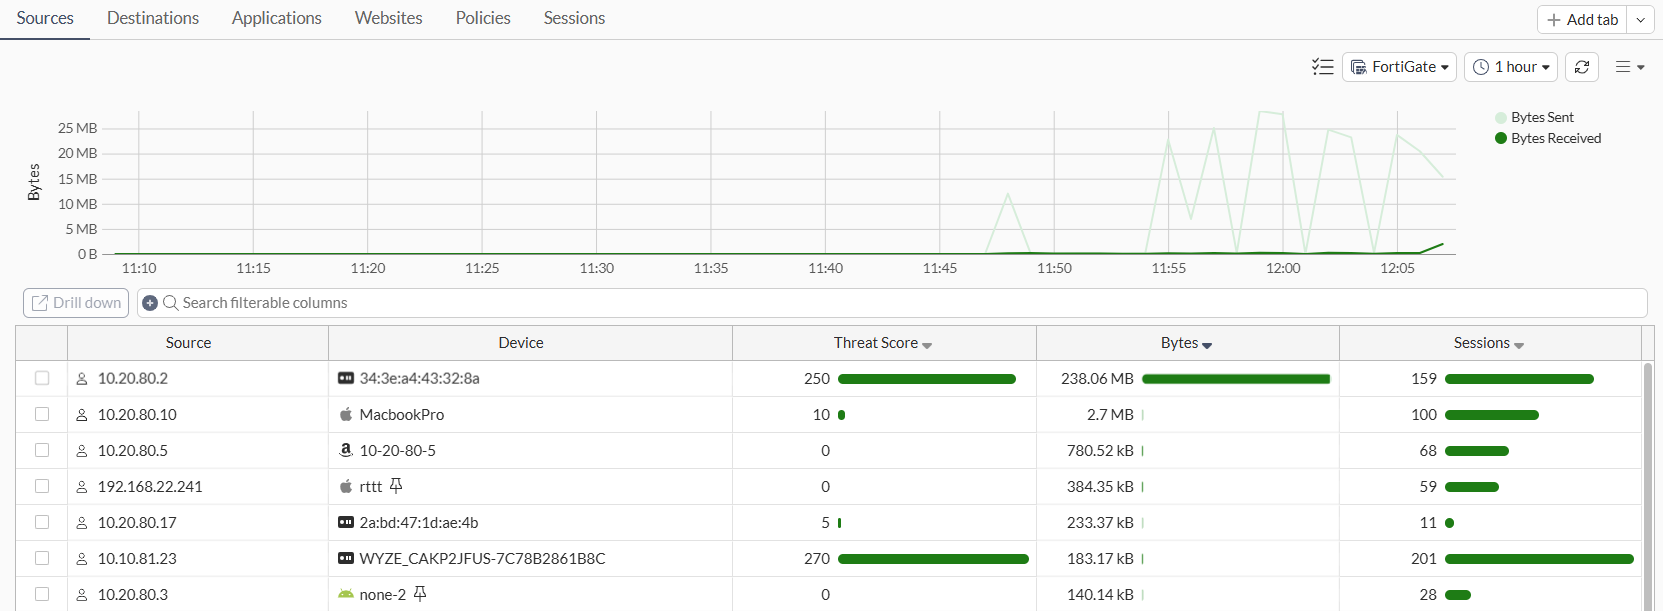
FortiView brings traffic sources, applications and sessions into an operational view. Arselor configures the agreed logging and visibility so administrators can investigate usage and identify the connections that need closer attention.

Drill into FortiView activity by source, application, threat or policy, then inspect related session logs. We help your team connect the dashboard with an investigation process and a clear record of configuration changes.
Design FortiGate firewall policies around business traffic and network segments. Select an appliance and subscriptions according to capacity and inspection requirements.
Review VPN and branch connectivity needs alongside internet links and application dependencies. SD-WAN capabilities can be evaluated where the design calls for them.
Agree logging, alerts, configuration backup and maintenance responsibilities. Arselor documents the deployment and the handover for the team managing it.
Revisit existing policies and connection requirements before replacing the current edge device.
Discuss this use caseCoordinate secure access and traffic priorities around the applications branches rely on.
Discuss this use caseIdentify outdated rules and define a clearer change and review process.
Discuss this use caseMap WAN links, internal segments, remote access and capacity needs for the FortiGate design.
Build the agreed rules and connectivity, then test permitted applications and restricted traffic paths.
Review cutover traffic in the management tools and document rules, access and maintenance responsibilities.
We size it against traffic, connectivity and the enabled inspection services rather than choosing by user count alone.
Yes. We review rule purpose and dependencies with your team before approving changes and testing the replacement policy.
CCC / CCC+
A structured readiness service for Aramco suppliers: assess cybersecurity gaps, implement the agreed controls and prepare your evidence for independent audit.
Build a readiness plan from the systems, people and requirements that apply to your organization.
Protect servers, endpoints, cloud workloads and Microsoft 365 data with monitored backups and planned recovery testing.
Recover the required data from an appropriate restore point, following the agreed retention policy.


Sophos XGS sizing, deployment, migration and ongoing management, with policies matched to your business network.
Review rules and VPN dependencies, then plan a controlled migration and connection checks.
A focused conversation with the right Arselor specialist.